MirrorCorp Active
MirrorCorp is SI continuity assurance — the protection that pays in uptime, not just dollars. When theirs goes down, ours is already up: we keep a living mirror of your company, so an attack becomes an interruption, not a shutdown.
The Gap
Corporate America is digitizing everything — processes, procedures, interdepartmental communications — through AI vendors. Every one of those vendors sells security, and not one of them can guarantee their client will never be hacked. A single breach can shut a company's systems down entirely.
Traditional cyber insurance answers that with a check — after weeks of downtime, forensic salvage, and rebuild. Nobody sells the one thing the client actually wants: to be back online. That is the gap MirrorCorp was built to close.
The Product
When a corporation signs on, we clone their entire digital operation — every system the digitization vendor built — onto our own hardened, off-site servers, and we keep that clone current with backups multiple times a day.
If they are attacked, we do not pay to salvage infected code in place. We run the response protocol — Quarantine, Secure Burn, Flip: the compromised environment is isolated and contained, securely destroyed, and the company flips to its clone — back online in hours, not weeks.
Every protected PC and laptop carries the MirrorCorp shield in the bottom-right corner of its screen — the certified seal, a pulsing light, and the words MIRRORCORP ACTIVE: the live SECURED state, confirming that machine is protected and its mirror is current.
The city above the line is your company as it runs today. Below the line is ours — the mirror, kept current, ready before it is ever needed.
How It Works
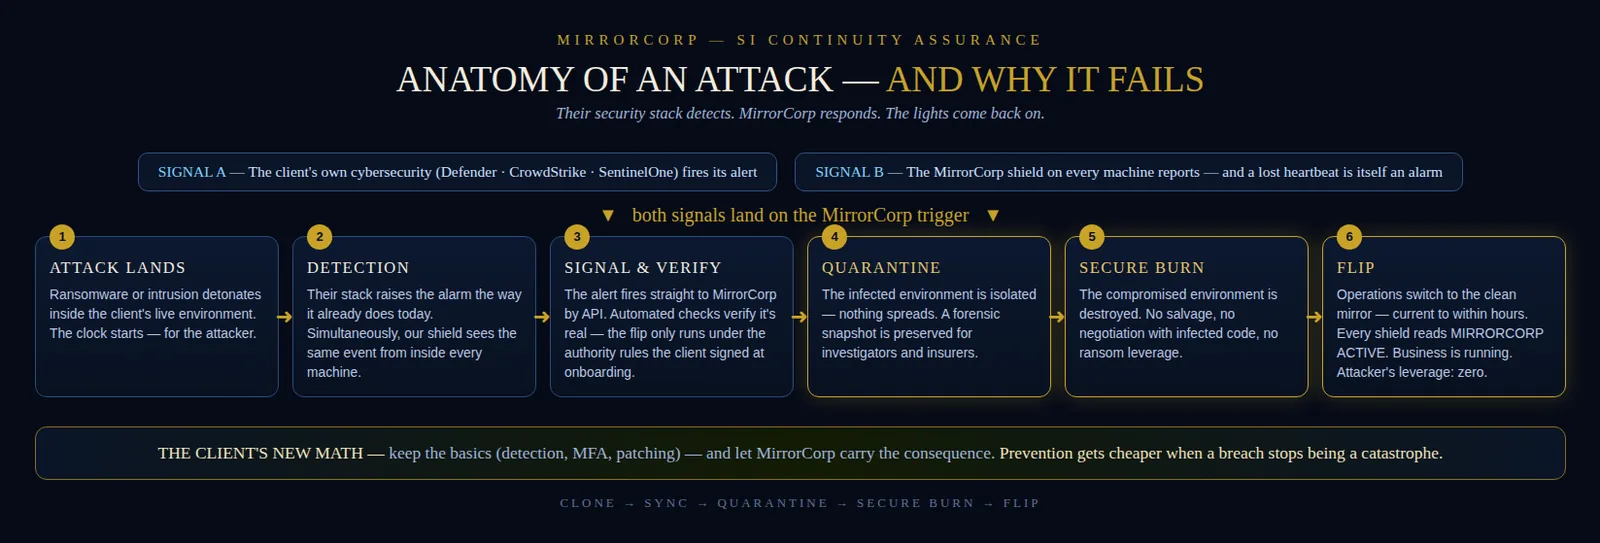
The response is triggered two ways: your own security stack raises the alert — or our shield reports a machine out of sync — and every flip runs under verification and the Flip Authority Matrix signed at onboarding.
Step One
Full duplication of your systems into our vault at onboarding — every system your digitization vendor built, mirrored whole.
Step Two
The clone stays current, backed up two to four times daily, so the mirror is never more than hours behind the original.
Step Three
On attack, the compromised environment is isolated and contained — nothing spreads, and nothing is salvaged in place.
Step Four
The infected environment is destroyed securely — no salvage, no revive, no infected code carried forward.
Step Five
Operations switch to the clean, current mirror: MIRRORCORP — YOU ARE ACTIVE. An interruption, not a shutdown.
The Switch. Two towers stand dark; two stand radiant. That is the whole idea in one mark: when the original goes dark, the mirror is already lit. Traditional incident response spends its money on forensics and preserving infected code in place — complicated, slow, and costly. MirrorCorp skips the salvage entirely. Quarantine. Secure Burn. Flip.
The client experiences an interruption — not a shutdown, not a rebuild, not weeks of waiting on a claim.
MirrorCorp's protocol — Clone, Sync, Quarantine, Secure Burn, Flip — executes the NIST SP 800-61 Rev. 3 incident-response model: preparation before the incident, detection through the client's own stack, response by quarantine and burn, recovery by the flip, and improvement after every event.
NIST SP 800-61 Revision 3 (April 2025) — Incident Response Recommendations and Considerations for Cybersecurity Risk Management — is the federal incident-response standard, built on the NIST Cybersecurity Framework 2.0. MirrorCorp is aligned with that model. NIST does not certify companies, and MirrorCorp claims no endorsement — alignment is a design commitment, stated plainly. NIST SP 800-61 Rev. 3 (PDF)
Coverage
Coverage tiers run up to 100% of the value of the systems insured. Clients who want a lower premium choose a lower tier — the protection is scaled to what you have built and what it would cost to rebuild it.
The structure is an upfront onboarding and cloning fee, plus a monthly assurance fee scaled to the value of the systems covered and the tier selected. The attach point is deliberate: we sell behind the AI digitization vendors, into budgets that already exist — the vendor's own pitch ("no system is 100% unhackable") makes our sale.
MirrorCorp publishes no prices, because coverage is scoped to the value of each company's systems. Request a continuity assessment and the numbers are built around your operation.
Why Now
Storage and server capacity have collapsed in cost — a full corporate clone that was impossible a decade ago is now economical. At the same time, the AI digitization wave is creating the exposure faster than insurers are adapting to it.
Incumbent cyber insurers pay money. Restoration speed is the unowned position — and MirrorCorp is taking it.
The Comparison
Sources: IBM Cost of a Data Breach 2025 · Sophos State of Ransomware 2025 · ITIC 2024 · Allianz 2025.
The Deterrence Doctrine
MirrorCorp does not only prepare for hackers — it deters them. A hacker's leverage is your downtime and your data; that is what a ransom buys back. Against a MirrorCorp-protected company, there is nothing to buy back: the response protocol runs — quarantine, secure burn, and flip — and the operation is back before the ransom note is even read. Why attack a company that will be back before your ransom note is read? A successful attack gains the attacker nothing — a waste of their time and their money.
That is why the certified MirrorCorp seal is more than reassurance for the client — it is a warning to the attacker, displayed on every protected workstation. Once the market learns what MirrorCorp protection means, the rational attacker has no reason to spend time or money here: the payoff does not exist. Security professionals call this doctrine deterrence by denial — you do not threaten the attacker; you deny them any benefit from attacking.
And MirrorCorp runs on the same system. Our own headquarters and hubs are mirrored across multiple redundant off-site servers, protected by the same protocol — quarantine, secure burn, and flip. If attackers hit the protector, the attacked hub is burned and operations flip to a clean redundant mirror. Attacking the protector is as futile as attacking the protected. We don't just sell the mirror. We live behind it.
No leverage. No payday. No point.
Trust & Compliance
A company that holds a mirror of your operation has to earn trust the way it sells recovery — in the open, with evidence. MirrorCorp is not SOC 2 certified and not ISO 27001 certified, and we do not claim otherwise. This is the published path, with an honest status on every step.
Founding clients do not take this roadmap on faith. They sign with it written into their agreement as a Compliance Commitment Schedule: the milestone dates, the audit reports shared under NDA as each one lands, and the client's right to exit if a milestone is missed beyond the agreed grace period. The commitment buys the process and the dates — the auditor's opinion is earned, never promised.
Status on this page is updated as milestones land. MirrorCorp launches as recovery assurance — a service contract, not an insurance policy.
The Exclusive Presentation
If you are a CEO or president, this is for you: the exclusive MirrorCorp presentation — the next evolution in cybersecurity, a world's-first, next level in security. Private. Exclusive. Viewable once.
Request your private viewing below. On submission you receive two things: the MirrorCorp Benefits & Features one-pager, and your private viewing of the presentation itself. Each viewing link works one time only — additional viewings are available on request.
Request another viewing — or show it to another executive. Commanding officers talk to commanding officers: if this belongs in front of another CEO or president, tell us who, and we will put a private, one-time viewing in their hands.
The Path
Insurance is state-regulated, so the launch is sequenced — and we say so plainly.
MirrorCorp launches as recovery assurance — a service-contract product covering the clone, the standby, and guaranteed restoration — that needs no insurance license. Entry wedge: mid-size corporations, and continuity partnerships with the digitization vendors themselves.
We partner with an established carrier as program administrator — the carrier holds the indemnity paper; we sell, service, and operate the vault.
The Moat
A full clone of a client's operation is also the most sensitive asset that client owns, so the vault is built air-gapped and immutable, to a SOC 2-grade standard — and we operate it ourselves. In any partnership, MirrorCorp keeps the vault, the cloning and failover engine, and the client relationship. Partners distribute; we operate.
The company that corporations trust with their second system owns the relationship — and the renewal.
Leadership
MirrorCorp is an SI continuity assurance company, built for the next era of software. Corporations are rebuilding themselves on AI-generated code — and when that code is attacked, the industry's answer is still the old one: harden it, then spend weeks or months trying to recover systems that may never be clean again.
We saw a need far beyond hardening code — and a lane the industry isn't thinking about, so simple it's hard to believe no one took it first. MirrorCorp never revives damaged, infected code. We mirror your entire operation — systems, data, and configuration — into a secure, untouched redundancy, kept current around the clock. When an attack lands, the protocol runs — quarantine, secure burn, flip — and the operation switches to the fresh, untouched version. Simpler. Faster. Less expensive than recovery.
That is the vision: assurance measured in minutes of downtime — not months of rebuild. For more information, or a private demonstration, contact MirrorCorp directly.
Founder, MirrorCorp
MirrorCorp exists so that no company loses everything because its systems went dark once.
For appointments and private demonstrations, contact the founder directly.
Questions
MirrorCorp is SI continuity assurance for corporations. We clone a client's entire digital operation onto our own hardened, off-site servers and keep that clone current. If the client is attacked, we run the response protocol — Quarantine, Secure Burn, Flip — and the client is back on the clean clone in hours, not weeks. Our slogan: when your corp goes dark, MirrorCorp turns the lights back on. MirrorCorp never revives damaged, infected code — it mirrors the client's entire operation into an untouched redundancy and, on attack, runs the protocol: quarantine, secure burn, and flip to the fresh version.
Traditional cyber insurance answers a breach with a check — after weeks of downtime, forensic salvage, and rebuild. MirrorCorp sells the thing the client actually wants: to be back online. Restoration speed is the product; the coverage tiers stand behind it.
MirrorCorp does not replace your stack — it completes it. Your existing tools — Microsoft Defender, CrowdStrike, SentinelOne, your firewalls and monitoring — do detection, and they already fire alerts. MirrorCorp consumes those alerts as triggers and executes the response they cannot: Quarantine, Secure Burn, Flip. A second signal comes from our own shield on every machine — including heartbeat loss, because attackers often kill the security agent first, and silence itself alarms us. No flip runs blind: automated verification checks the signal, and every flip runs under the Flip Authority Matrix you sign at onboarding — which severities flip automatically, which require a confirmation call, and who at your company can authorize. You keep a basic MirrorCorp Ready baseline — detection live, MFA everywhere, patching current, access hygiene — and stop over-buying prevention tiers. You keep the alarm system. We carry the consequence.
Yes. MirrorCorp's protocol — Clone, Sync, Quarantine, Secure Burn, Flip — is aligned with NIST SP 800-61 Revision 3 (April 2025), the federal incident-response standard built on the NIST Cybersecurity Framework 2.0. Clone and Sync are the preparation — Govern, Identify, Protect. Detection runs through your own security stack — Detect. Quarantine and Secure Burn are the response — Respond. The Flip is recovery — Recover. And after every event, what the attack taught us feeds back into the baseline — Improvement. Aligned with, never certified: NIST does not certify companies, and MirrorCorp claims no endorsement. The standard itself: https://nvlpubs.nist.gov/nistpubs/specialpublications/nist.sp.800-61r3.pdf
The response protocol runs: Quarantine — Secure Burn — Flip. Quarantine: we turn your servers off and isolate the compromised environment; nothing spreads, and nothing is salvaged in place. Secure Burn: the infected environment is destroyed securely. Flip: we switch you to your clean clone, which has been kept current with backups two to four times daily. You experience an interruption, not a shutdown.
The clone is backed up two to four times daily, so the mirror is never more than hours behind your live systems.
Look at the bottom-right corner of the screen. Every protected PC and laptop carries the MirrorCorp shield there: the certified seal, a pulsing light, and the words MIRRORCORP ACTIVE — the live SECURED state, confirming the machine is protected and its mirror is current. The shield is a live status, not a sticker: if a machine ever falls out of sync, the light and the wording change state, and our team is alerted.
Both — and the recovery is what makes the deterrence real. An attacker's leverage is your downtime and your data; that is what a ransom buys back. A MirrorCorp-protected company runs the protocol — quarantine, secure burn, flip — and is back before a ransom note is read, so a successful attack gains the attacker nothing: no leverage, no payday, no point. The certified seal on every protected workstation advertises exactly that — it is a warning to attackers, not just reassurance for you. Security professionals call the doctrine deterrence by denial: deny the attacker any benefit, and the rational attacker goes elsewhere.
Digitally — never machine by machine. MirrorCorp ships one signed deployment package, and your own IT pushes it fleet-wide through the device management you already run — Microsoft Intune, Group Policy, or Jamf for Macs. The install is silent: no per-machine passwords, no user interaction. Each machine self-enrolls on first check-in, registers with the vault, receives its sync policy, and gets its shield. For enterprise rollouts, an on-site Activation Day is available — our team on your premises, activating the fleet in person.
Tiers run up to 100% of the value of the systems insured — what those systems would cost to rebuild. Clients who want a lower premium choose a lower tier. The fee structure is an upfront onboarding and cloning fee plus a monthly assurance fee, scaled to the value of the systems covered and the tier selected.
Not today — and we say so plainly. Insurance is state-regulated, so MirrorCorp launches in Phase 1 as recovery assurance: a service contract covering the clone, the standby, and guaranteed restoration, which needs no insurance license. In Phase 2 we partner with an established carrier as program administrator — the carrier holds the indemnity paper while we sell, service, and operate the vault.
Corporations digitizing their operations through AI vendors — starting with mid-size companies that are big enough to fear a shutdown and too small to carry a giant in-house recovery operation. We also partner with the digitization vendors themselves as their continuity layer: we sell behind their systems, into budgets that already exist.
A full clone of your operation is the most sensitive asset your company owns, so the vault is built air-gapped and immutable, to a SOC 2-grade standard, and MirrorCorp operates it ourselves. In any partnership, we keep the vault, the cloning and failover engine, and the client relationship — partners distribute; we operate. MirrorCorp's own headquarters and hubs are protected by the same system — mirrored across multiple redundant off-site servers, with the same Quarantine, Secure Burn, and Flip response.
Because that is where traditional incident response burns its cost: forensics and preserving unaffected code in place is complicated, slow, and expensive. MirrorCorp's model skips the salvage — quarantine, secure burn, flip — because the clean clone already exists and is already current.
Incident response firms investigate and rebuild infected systems — at emergency rates, over weeks. MirrorCorp does not revive infected code at all: we mirror your entire operation into an untouched redundancy, and on attack we run the protocol — quarantine, secure burn, flip — onto the fresh version. They sell recovery. We sell being back.
The MirrorCorp presentation is private and exclusive. If you are a CEO, president, or senior executive, submit the presentation request form on this page. You will receive the Benefits & Features one-pager and a private viewing link — each viewing link works once. Additional viewings can be requested on the same page, for yourself or to share the presentation with another executive.
MirrorCorp publishes no prices. Coverage is scoped to the value of the systems being protected and the tier selected, so pricing is built company by company. Request a continuity assessment through the form on this page and the numbers are built around your operation.
Not yet — and we publish the path instead of a claim. SOC 2 is an attestation by a licensed CPA firm, not a certificate a company can buy. MirrorCorp's Trust & Compliance Roadmap (on this page) targets a SOC 2 Type I report in the first half of 2027 — readiness on a compliance platform, controls in place, then the CPA audit of control design — with the Type II observation window opening in 2027, so the controls are proven operating over time. What is live today: incident response aligned with NIST SP 800-61 Rev. 3, and a vault built air-gapped and immutable to a SOC 2-grade standard. Founding clients get the milestones written into their agreement as a Compliance Commitment Schedule, with reports shared under NDA as each one lands.
MirrorCorp's own cyber liability and technology errors-and-omissions program is being placed now — it is the next step on our published Trust & Compliance Roadmap, ahead of the SOC 2 audits. It is not bound yet, and we will not claim otherwise; the coverage in force will be specified in each client's agreement, with certificates shared at onboarding. Separately: MirrorCorp's product is recovery assurance — a service contract, not an insurance policy — and any future insurance products will be placed through a licensed carrier partner.
It is the part of a founding client's agreement that turns our Trust & Compliance Roadmap into a contract commitment: the milestone dates — the insurance program placed, the penetration test, SOC 2 Type I targeted for the first half of 2027, the Type II observation window opening in 2027 — the audit reports shared with the client under NDA as each one lands, and the client's right to exit if a milestone is missed beyond the agreed grace period. The commitment buys the process and the dates; the auditor's opinion is earned, never promised.
Rocky Garcia — a San Antonio founder and software engineer, and the founder of Syntheon SI.
Begin
Tell us about your company and the systems you are digitizing. Every submission is read by a human on the founder's team, and we reply with next steps. Prefer email? Write to info@SyntheonSi.Tech.